Important things to know
If you are contemplating starting a career in cybersecurity but feel stuck on which role to begin with, then this article is for you.
Cybersecurity is one of the fastest-growing fields in IT today. Organizations are investing heavily in security to protect against data breaches and cyberattacks. However, when people begin exploring the industry, they often encounter job roles and titles that can be confusing.
Two roles are commonly discussed as entry points into cybersecurity:
- SOC Analyst
- GRC Analyst
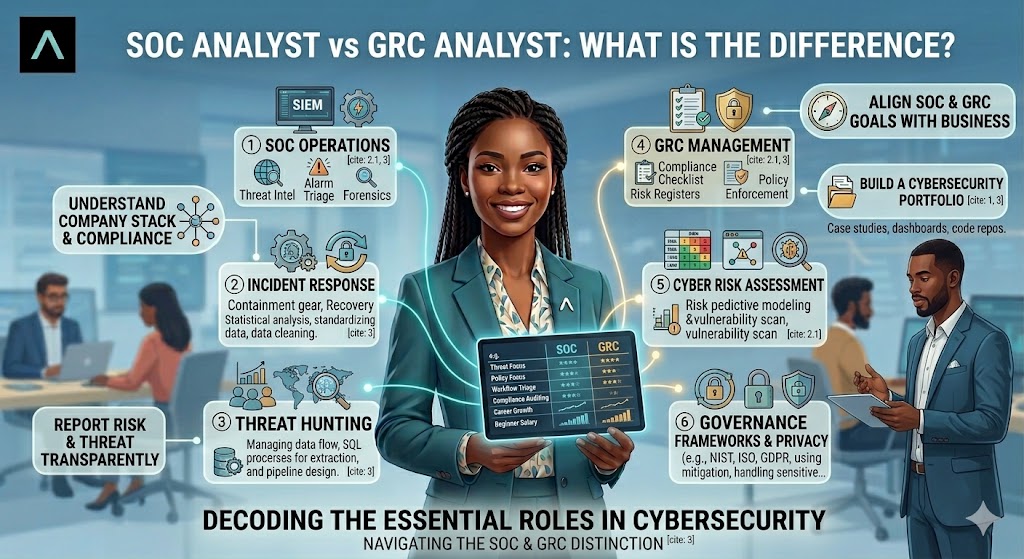
Both roles help protect organizations from cyber threats but they do so in very different ways.
One focuses on monitoring systems, detecting threats, and responding in real time, while the other focuses on policies, risk management, and regulatory compliance.
So, what exactly is the difference?
Let’s break it down.
Who is a SOC Analyst?
A SOC Analyst (Security Operations Center Analyst) is a frontline defender against cyberattacks.
SOC analysts work in a Security Operations Center (SOC), where they continuously monitor security alerts, detect threats, analyze incidents, and respond to attacks.
This role is highly technical and requires a strong understanding of cybersecurity tools, attack techniques, and defensive strategies.
Typical Responsibilities of a SOC Analyst
- Monitoring security tools such as SIEM platforms
- Investigating alerts and suspicious network activity
- Analyzing logs and security events
- Responding to incidents like malware infections or unauthorized access
- Escalating major incidents to incident response teams
- Conducting threat hunting and basic forensic analysis

SOC analysts are the people who actively watch the network and take action whenever something suspicious happens.
You will find our previous article very useful, especially if you are in the job application phase.
Fastest Way To Become a SOC Analyst: Certifications or Internships?
What is a GRC Analyst?
Rather than responding to attacks directly, GRC analysts ensure that an organization:
- Follows security policies
- Complies with regulatory requirements
- Manages risks effectively
They play a crucial role in aligning security practices with business goals and industry standards.
Key Responsibilities of a GRC Analyst
- Developing and maintaining security policies and procedures
- Ensuring compliance with standards (e.g., ISO 27001, GDPR, NIST)
- Conducting risk assessments and audits
- Identifying and mitigating organizational risks
- Collaborating with technical teams to enforce security controls
GRC analysts ensure the organization is secure by design, not just by reaction.
SOC vs GRC: Key Differences
| Area | SOC Analyst | GRC Analyst |
| Focus | Threat detection & response | Risk management & compliance |
| Nature of Work | Technical, hands-on | Strategic, policy-driven |
| Tools | SIEM, EDR, IDS/IPS | Frameworks, policies, audit tools |
| Work Style | Real-time monitoring | Documentation & assessments |
| Goal | Stop attacks | Prevent risk and ensure compliance |
Which One Should You Choose?
Choosing between SOC and GRC depends on your interests and strengths.
Choose SOC if you:
- Enjoy hands-on technical work
- Like investigating incidents and solving problems
- Are interested in threat detection and defense
- Prefer fast-paced, real-time environments
Choose GRC if you:
- Enjoy documentation, structure, and governance
- Like working with policies and frameworks
- Are interested in risk management and compliance
- Prefer a less technical, more strategic role
Both SOC and GRC roles are critical to an organization’s cybersecurity posture. One is reactive and technical, while the other is proactive and strategic.
There is no “better” role, only what aligns best with your skills, interests, and long-term goals.
If you're just starting out, the key is to understand both paths, try small projects in each area, then commit to the one that fits you best.
To learn more about which path suits you and aligns with your previous experience, book a free clarity call with our Consultants and they will offer tailored guidance to help you get started in the industry and land your dream cybersecurity job. Click here


